Step 01
Assess
Map the workflows in scope, the people who run them, and the decisions a person still has to make.
HIPAA compliant AI for medical practices: BAA checklist, PHI rules, and how to check a vendor before anyone enters patient information. This is not legal advice.
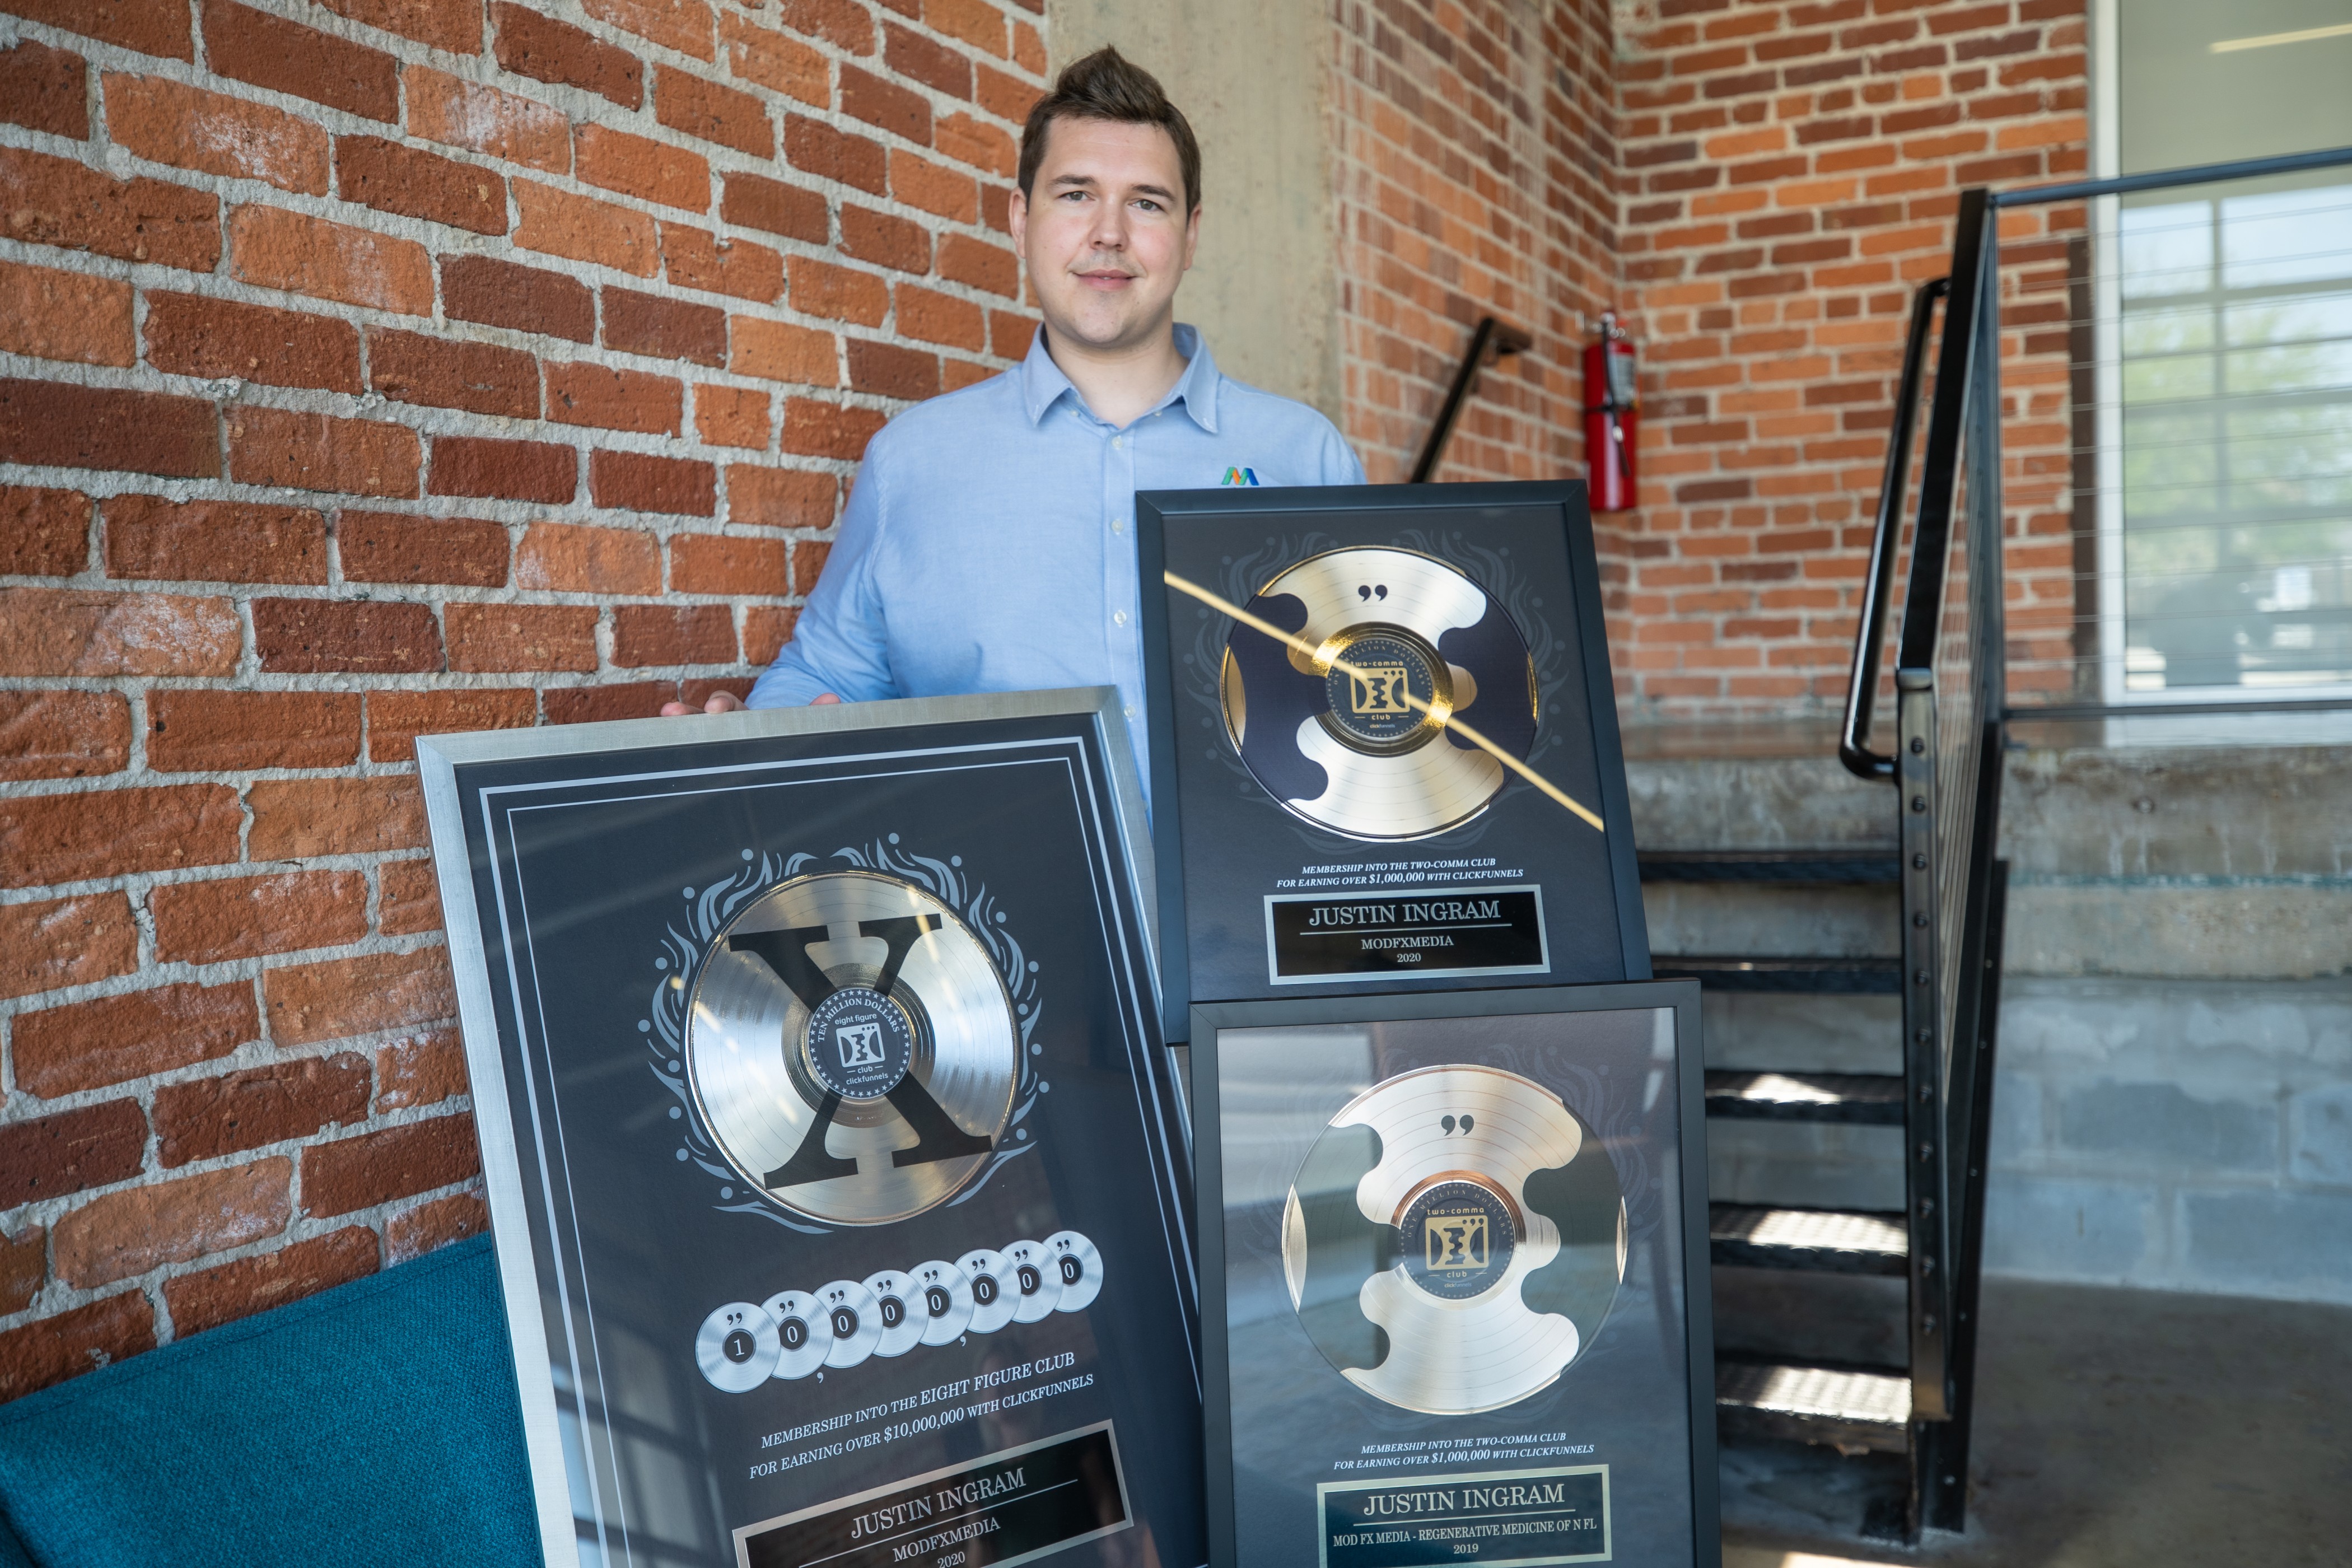 Written & reviewed by Justin Ingram, Healthcare AI ConsultantLast reviewed August 2026
Written by Justin Ingram, healthcare AI consultant. Reviewed November 9, 2026.
Every medical practice that wants to use AI has to answer a practical question: which product, which plan, and which settings are allowed to see patient information? A vendor may offer a Business Associate Agreement. That agreement does not, by itself, make every feature or every staff habit appropriate.
I wrote this for clinic owners, practice administrators, and operations leaders. It is an explanation of how I review a tool before anyone enters patient information. It is not a legal opinion and it is not a certification of any product.
I am Justin Ingram. I opened my first clinic in 2017. If the question is how a multi-site group should sequence this work, start with healthcare AI consulting, the executive workflow assessment, or healthcare operations consulting. The discovery form is the AI readiness assessment.
The AI vendor that will see patient information needs a signed BAA before that use. A missing BAA is a stop. This page is not a legal opinion.
PHI must be encrypted in transit and at rest. The vendor must have access controls, audit logging, and breach notification procedures. Data must not be used to train AI models unless explicitly permitted by the covered entity.
Even with a BAA, practices must implement policies governing how staff use AI tools: what information can be entered, how outputs are reviewed, and how errors are corrected.
Prefer HIPAA-eligible cloud environments (for example AWS or Azure with a BAA), clear data retention settings, and the ability to delete PHI on request. Marketing claims like "enterprise secure" are not a substitute for these controls.
A large language model is not automatically appropriate for patient information. Consumer ChatGPT, Claude, Gemini, and similar products need the vendor's current eligible-product list, a signed BAA, and the settings that list requires. An "enterprise" label by itself is not that list.
HIPAA-compliant LLMs and HIPAA-compliant AI platforms typically add: signed BAA, no training on your PHI by default, encryption, audit logs, role-based access, and often private or tenant-isolated deployment options.
If your team is asking "is ChatGPT HIPAA compliant?" or "is Claude AI HIPAA compliant?", read the vendor's current list before anyone enters patient information. OpenAI's help center, checked November 8, 2026, lists ChatGPT for Healthcare, ChatGPT for Clinicians, ChatGPT for Enterprise with Regulated Workspace, ChatGPT FedRAMP, API with Modified Retention, and API FedRAMP with Modified Retention as HIPAA-eligible when a BAA is in place (HIPAA eligible products and functionality). The same check says ChatGPT Team is not on that list. OpenAI also says it does not offer a BAA for ChatGPT Business (Getting a BAA for the OpenAI API). Free, Go, Plus, Pro, and consumer Health are not on the eligible list either. This is not legal advice. Confirm the current page and your own agreement before use.
1) BAA available before go-live, not "after we sign the contract." Read the BAA; confirm subprocessors and breach timelines.
2) PHI training policy in writing: your data is not used to train foundation models unless you opt in.
3) Encryption in transit (TLS 1.2+) and at rest, plus access controls and immutable audit logs.
4) EHR / practice-management integration path that does not force PHI into shadow tools (personal Gmail, Slack free, consumer Notion).
5) Staff workflow: who can paste what, how notes are reviewed, and how mistakes are corrected before they hit the chart.
6) Offboarding: export and delete PHI when you leave the vendor. If they cannot answer this cleanly, do not buy.
ChatGPT for Healthcare (OpenAI): Listed by OpenAI as HIPAA-eligible when a BAA is in place and configuration rules are followed. Consumer Free/Go/Plus/Pro, ChatGPT Business, ChatGPT Team, and consumer Health are not BAA-eligible. Suitable for clinical documentation, patient communication drafting, and operational tasks when used on an eligible product.
Claude for Healthcare (Anthropic): Available through the API with enterprise agreements. Strong for clinical reasoning, documentation, and complex analysis tasks.
BastionGPT: Built specifically for healthcare. HIPAA compliant by design with BAA included. Offers clinical documentation, patient communication, and practice management AI features.
CompliantChatGPT: A HIPAA-compliant AI medical copilot designed for healthcare professionals. BAA included. Focused on clinical workflows and secure PHI handling.
Hathr.AI: Healthcare-specific AI platform with built-in compliance. Offers AI scribe functionality, clinical decision support, and practice management tools.
GoHighLevel: CRM and marketing automation platform. Offers BAA for healthcare clients. AI features include conversational AI agents and automated communication.
Ambient AI scribes (Abridge, Nabla, and peers): Several medical scribe vendors offer BAAs and EHR integrations. Treat each as its own vendor risk review — see our AI scribe for doctors guide for deployment detail.
Standard ChatGPT (free or Plus plans): Does not offer a BAA. Any PHI entered into the standard ChatGPT interface is a potential violation. Many practices make this mistake unknowingly.
Standard Claude (consumer product): The consumer version does not include BAA coverage. Healthcare organizations need the enterprise API with explicit BAA.
Google Gemini (consumer version): Not HIPAA compliant in its standard form. Google offers HIPAA-eligible services through Google Cloud with BAA, but the consumer Gemini product is not covered.
Personal productivity apps without a BAA (consumer Notion, free Zapier, personal Dropbox, consumer email): Convenient, and still a compliance gap if PHI flows through them.
Using the free version of ChatGPT with patient information. Copying patient data into AI tools that lack BAAs. Failing to include AI tools in your practice's security risk assessment. Assuming a tool is compliant because it claims to be "secure." Not updating BAAs when AI vendors change their terms of service.
Letting staff use personal AI accounts on clinic devices. Pasting full charts into a "safe sounding" tool that has no BAA. Skipping staff training so the tool is compliant on paper but unsafe in daily use.
Assessment: Map where PHI touches AI today (scribe, chat, scheduling, billing, marketing). Flag non-compliant tools immediately.
Build: Select BAA-backed vendors, configure retention and access, connect EHR/scheduling carefully, and write SOPs your staff will actually follow.
Optimise: Re-check the written scope, the BAA, and who reviews the output. Expand only after those gates still hold.
If you want a guided path, start with the free AI readiness assessment or our healthcare AI consulting engagement. For a productized tool list, see the HIPAA-compliant AI tools directory.
AI is HIPAA compliant only when three conditions are true at the same time: (1) every vendor that creates, receives, maintains, or transmits PHI has a signed Business Associate Agreement with your practice; (2) technical safeguards are in place — encryption in transit and at rest, access controls, audit logs, breach notification; (3) your staff follows written use policies so PHI never lands in consumer AI accounts.
Marketing language like "bank-grade security," "SOC 2," or "enterprise ready" does not equal HIPAA compliance. SOC 2 can support a vendor review, but without a BAA and PHI handling rules, the tool is still unsafe for patient data.
Generative AI and LLMs follow the same rule: the model is only as compliant as the product plan, contract, and settings around it. Free ChatGPT, Claude consumer apps, and Gemini consumer apps are not HIPAA compliant AI for PHI — period.
Therapists and behavioral health practices need the same BAA layer plus stronger privacy culture: session notes, intake forms, and portal messages are PHI. Prefer vendors that offer BAAs for notes, scheduling, and messaging — not a consumer chatbot wrapped in a therapy brand.
HIPAA compliant AI transcription and ambient listening are high-risk if the audio or transcript trains a public model. Require written "no training on your PHI," retention limits, and a delete path before you turn the mic on.
Be careful with "free HIPAA compliant AI" claims. Free tiers almost never include a BAA. If the product is free and accepts clinical text, treat it as non-compliant until legal and security review says otherwise.
For therapists evaluating stacks, start with documentation and scheduling leaks, then expand. Pair this guide with AI for behavioral health and our HIPAA-compliant AI tools directory.
There is no single "best HIPAA compliant AI" for every clinic. The right stack depends on specialty, EHR, staffing, and which workflow burns the most hours first — usually charting, missed calls, no-shows, or A/R.
Score vendors on: BAA before go-live, PHI training policy, audit logs, EHR fit, staff adoption risk, and offboarding. Then run a 30-day pilot on one workflow with success metrics (hours saved, show rate, denial rate).
Justin Healthcare AI does not sell a single LLM brand. We install operator stacks: compliant tools + SOPs + training so your team stops pasting charts into unsafe apps. The point is that the team keeps using the workflow after the first week.
A healthcare AI consultant helps a practice identify the workflow, check the vendor, and implement only after a signed BAA and a written scope. That is not a promise that a product is HIPAA compliant.
Justin Ingram opened and ran medical practices starting in 2017 before moving into healthcare AI consulting. That distinction matters. Most "AI consultants" have never run a P&L inside a clinic or dealt with a no-show problem at 8am on a Monday. HIPAA handling is part of the recommendation, not something added after a vendor complaint.
Map every workflow, score AI readiness across 5 dimensions, and surface the highest ROI opportunities. Every engagement starts with our free AI readiness assessment.
A prioritized implementation plan with ROI projections and a full HIPAA compliance review, built alongside your team.
Configure the accepted workflow and train the people who use it. This is not a promise of hours or revenue.
Look for three things before signing anything with any healthcare AI consultant:
1. A signed BAA requirement for every recommended vendor, not just "HIPAA-friendly" marketing language
2. An operator background. Someone who's actually run a practice, not just sold software into one
3. A fixed deployment timeline with measurable outcomes, not an open-ended "ongoing strategy" retainer with no end point
A proven approach to help healthcare practices adopt AI with confidence and achieve measurable growth.
Map the workflows in scope, the people who run them, and the decisions a person still has to make.
Write what will change, what stays manual, and which steps need a signed BAA before they proceed.
Configure only the accepted workflow and train the people who use it. A wider rollout needs a new scope.
Tell us about your practice and we'll show you exactly where AI can save you time and money.
HIPAA compliant AI is any artificial intelligence system that can lawfully process protected health information because the vendor will sign a Business Associate Agreement and implements required safeguards: encryption, access controls, audit logging, breach notification, and restrictions on using PHI to train models.
Three things together: a signed BAA with every PHI-touching vendor, technical safeguards (encryption, access control, audit logs), and staff policies that keep PHI out of consumer AI tools. Security marketing alone is not enough.
OpenAI's help center, checked November 8, 2026, lists ChatGPT for Healthcare, ChatGPT for Clinicians, ChatGPT for Enterprise with Regulated Workspace, ChatGPT FedRAMP, and certain API plans with Modified Retention as HIPAA-eligible when a BAA is in place (https://help.openai.com/en/articles/20001069-hipaa-eligible-products-and-functionality). ChatGPT Team is not on that list. OpenAI also says it does not offer a BAA for ChatGPT Business (https://help.openai.com/en/articles/8660679-getting-a-business-associate-agreement-for-the-openai-api). Free, Go, Plus, Pro, and consumer Health are not on the eligible list. This is not legal advice. Check the current OpenAI page before any patient information is entered.
Rarely in any form you should trust with PHI. Free consumer AI products almost never include a BAA. If a vendor claims "free and HIPAA compliant," demand the BAA and legal review before any patient data is entered.
A BAA is a legal contract between a covered entity (your practice) and a vendor (the AI tool company) that establishes the vendor's responsibilities for protecting PHI under HIPAA regulations.
Many ambient AI scribes offer BAAs and EHR integrations, but compliance is vendor-specific. Confirm BAA, retention, and training policies before go-live. See our AI scribe for doctors guide for comparison criteria.
The legal bar is the same, but therapy workflows are note-heavy and privacy-sensitive. Prioritize BAAs for documentation, scheduling, and messaging, and ban consumer AI for session content.
Entering patient information into a tool that is not covered by your BAA can create a HIPAA problem. What happens next depends on the facts. Ask your counsel. This page is not a legal opinion.
At minimum quarterly. AI vendors frequently update their terms of service, data handling practices, and compliance certifications. What was compliant six months ago may not be today.
Yes. Every AI vendor that processes PHI requires its own BAA. You cannot rely on one vendor's BAA to cover another vendor's tool.
A HIPAA compliant LLM is one type of HIPAA compliant AI. You still need BAAs, access controls, and safe workflows around any model that touches PHI — whether it is a chatbot, scribe, or automation agent.
The discovery call names the workflows in scope. You can accept the written scope, revise it, or stop.
Discovery call. No patient information on the form.
BAAs, PHI handling, vendor checklists, and safe AI stacks for clinics. Explore cluster guides in this silo, then jump to sibling pillars.
Disclaimer:The consulting services described on this page are advisory and operational in nature. They do not constitute medical advice, clinical decision-making support, or legal advice. AI implementation decisions should involve your practice's clinical, compliance, and legal stakeholders. This page does not publish client results. An example is not a promised outcome.
Discover how AI can reduce admin, improve patient experiences, and help your practice grow with confidence.
Ready when you are. Free audit
Book audit